
Elementor CSRF flaw lets attackers hijack WordPress sites via crafted link
This digest was compiled by AI from multiple sources — links to the originals are below.
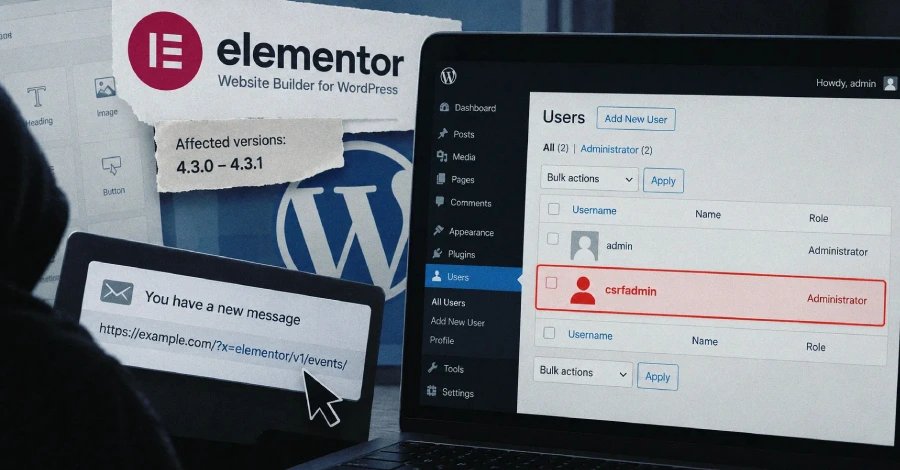
A high-severity CSRF flaw in Elementor Website Builder versions 4.3.0 and 4.3.1 lets unauthenticated attackers create rogue admin accounts after a logged-in admin clicks a crafted link. The flaw carries a CVSS score of 8.8 and affects over 2 million WordPress sites. Patchstack disclosed the issue, which is fixed in version 4.3.2.
Key Facts
- The CSRF vulnerability affects only Elementor Website Builder versions 4.3.0 and 4.3.1, which are installed on more than 2 million WordPress sites.
- The flaw carries a CVSS score of 8.8 out of 10.0 and has not yet been assigned a CVE identifier.
- Patchstack credited a security researcher using the alias "Saggre" with discovering and reporting the bug.
- The vulnerability was fixed in Elementor version 4.3.2, released earlier this week.
- The bypass applies to the entire REST API surface of a site, including WordPress core routes and routes of every other installed plugin.
Vulnerability Mechanics
The flaw stems from the Editor Events module skipping CSRF protection for cookie-authenticated REST API requests whenever the literal string "elementor/v1/events/" appears anywhere in the request URI. Because the request URI includes the query string, and the query string is written by whoever composes the link, any REST request can opt itself out of that protection by appending a harmless-looking parameter. The attack does not hinge on any prerequisite, such as JavaScript, a submitted form, or a web page under the threat actor's control. The link can even be a plain anchor tag embedded in an email, a chat message, or a comment.
Exploitation and Impact
On a stock installation, an administrator clicking the link creates a second administrator account for the attacker. An attacker could exploit this loophole to create an administrator account through "/wp/v2/users" using a crafted request. The bypass applies to the entire REST API surface of a site, including WordPress core routes and the routes of every other plugin installed on it. Elementor releases before 4.3.0 do not ship the Editor Events proxy, so they are not affected by the flaw.
Disclosure and Remediation
Patchstack disclosed the vulnerability after responsible disclosure, and the issue has been addressed in version 4.3.2 released earlier this week. A security researcher going by the alias "Saggre" has been credited with discovering and reporting the bug. Users of the plugin are advised to apply the latest update as soon as possible to counter any potential threat.
1 source
Time · lag behind first